At the end of this page, you can find the full list of publications and patents.
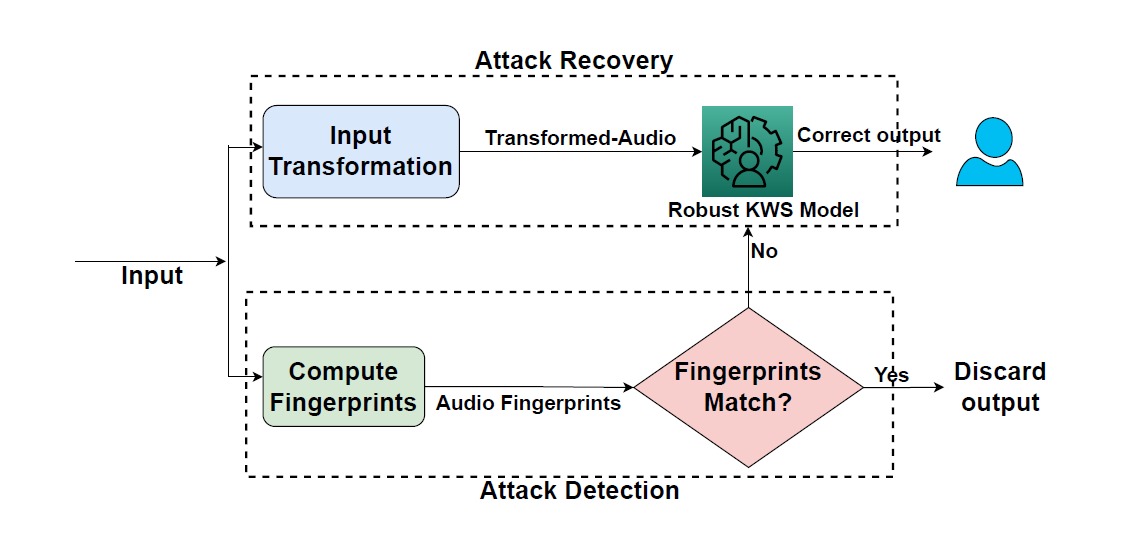
IoT devices (e.g., voice assistants) that execute real-time speech commands are proliferating fast in our daily lives. In such a device, detecting the correct keyword spoken as a command triggers the supported function, and hence keyword spotting (KWS) using a machine learning (ML) model is the pivotal task in their functioning. However, KWS is vulnerable to adversarial machine learning (AML)-based attacks through which an adversary can craft an adversarial…
Mehreen Jabeen, Vireshwar Kumar, Rijurekha Sen
ACM AsiaCCS 2024
CORE A
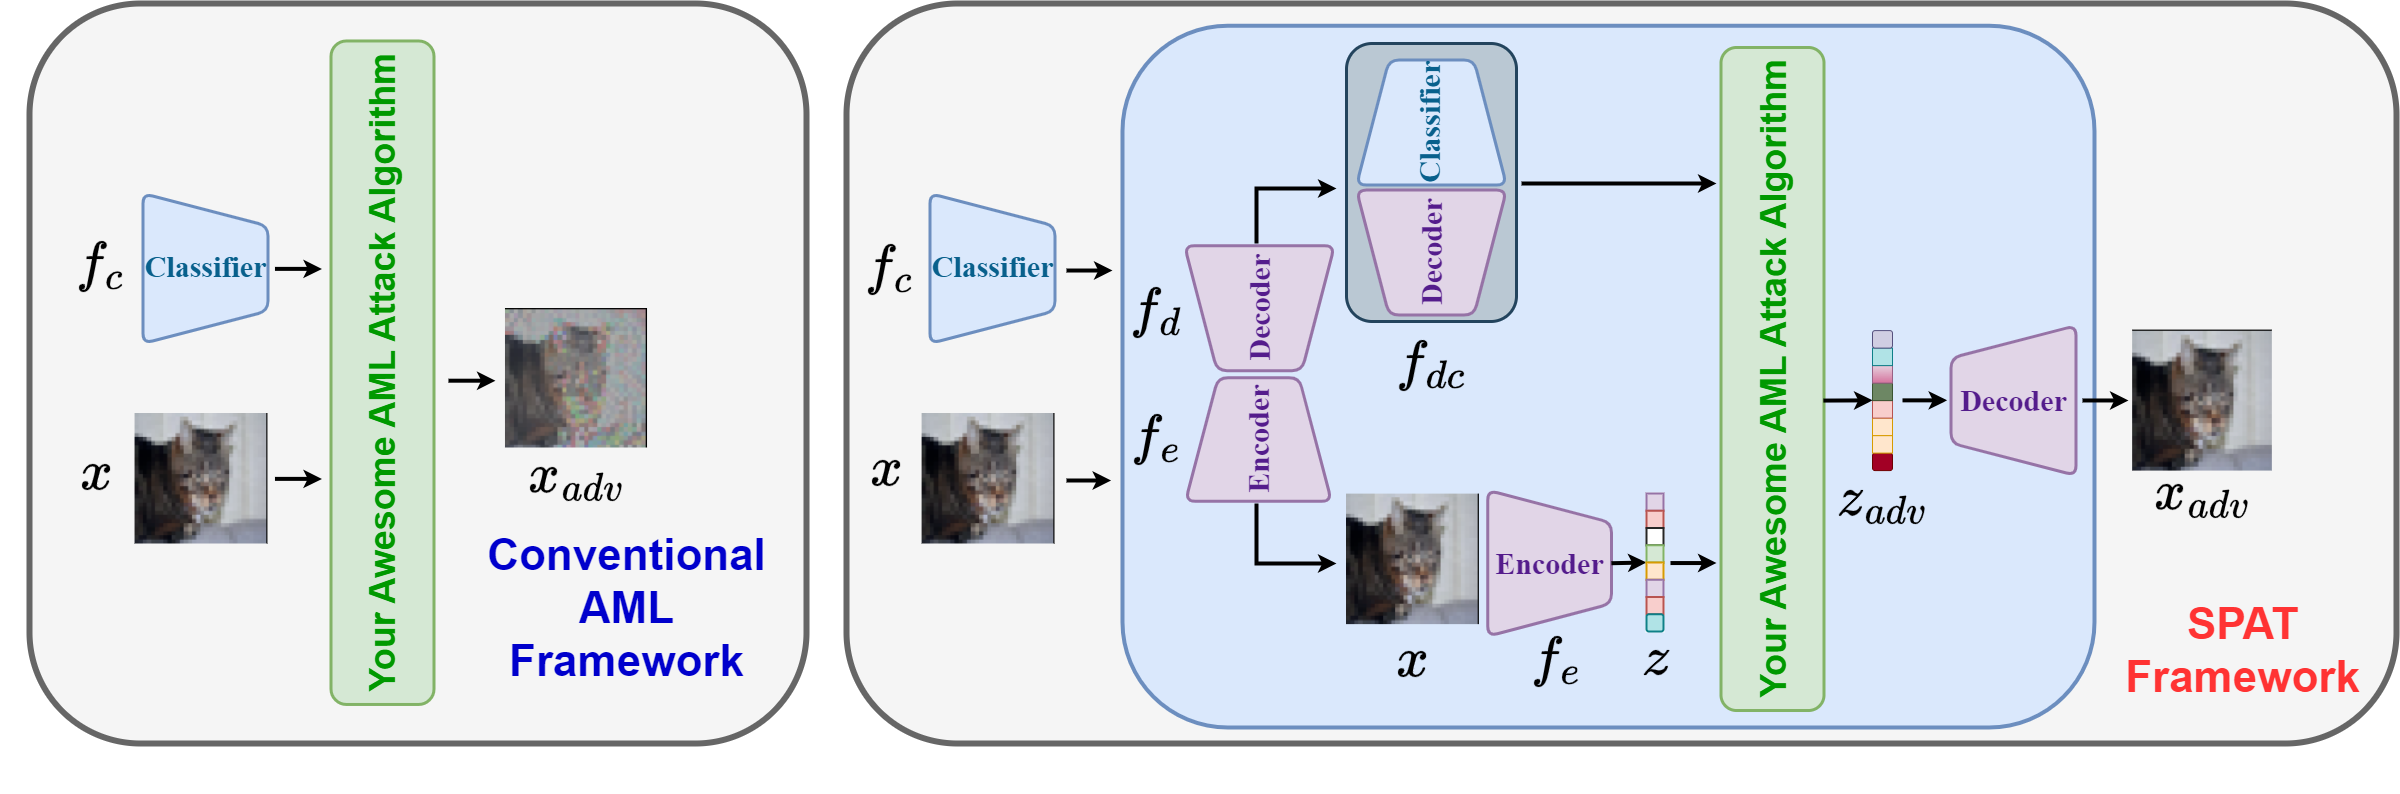
Machine Learning(ML) models are vulnerable to adversarial machine learning(AML) attacks, which generate adversarial examples by adding well-crafted perturbations to the benign examples. If the perturbations are added without considering the semantic correctness, the attack can be easily detected. We introduce SPAT, a unified framework that transforms conventional AML attacks into semantic-preserving versions while maintaining a comparable attack success rate.
Subrat Kumar Swain, Vireshwar Kumar, Dan Dongseong Kim, Guangdong Bai
ECAI 2023
CORE A
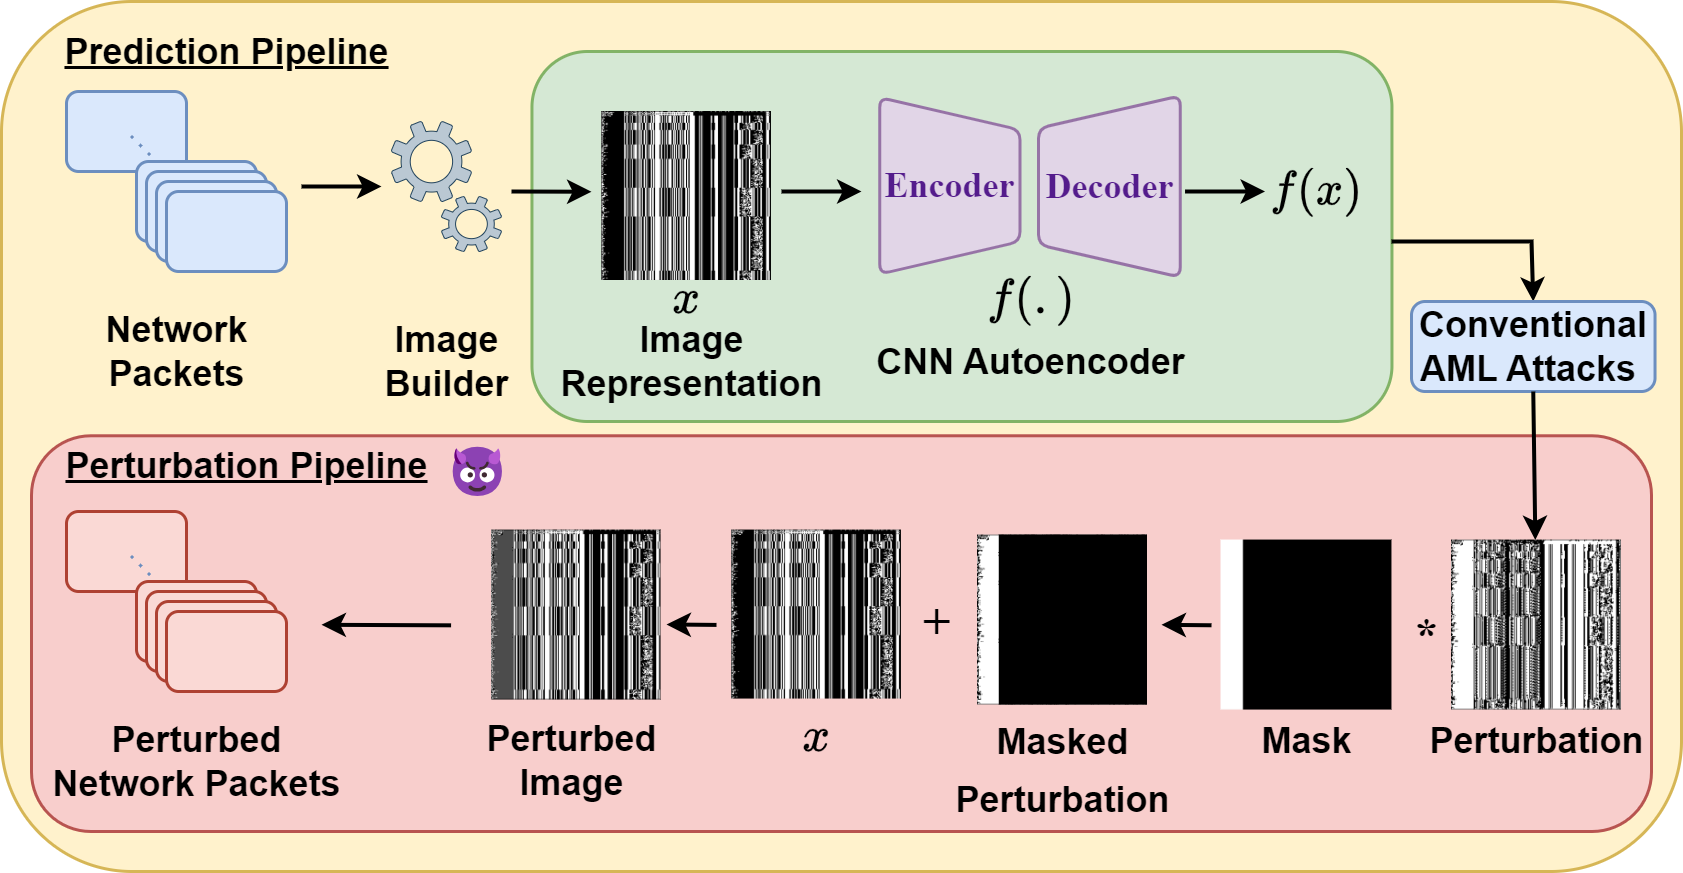
While adversarial machine learning (AML) attacks have become prevalent in the computer vision (CV) domain, their applications in other domains, such as network intrusion detection systems (NIDS), remain limited. This gap stems from the lack of a well-defined input space in non-image domains, hindering the generation of adversarial examples. Unlike CV problems, where the input space is the feature space, other domains generally lack a precise inverse mapping from the feature space to the problem …
Subrat Kumar Swain, Vireshwar Kumar, Guangdong Bai, Dan Dongseong Kim
DSN Disrupt 2024
CORE A
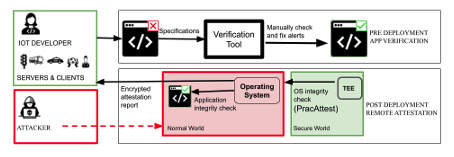
Machine Learning (EdgeML) algorithms on edge devices facilitate safety-critical applications like building security management and smart city interventions. However, their wired/wireless connections with the Internet make such platforms vulnerable to attacks compromising the embedded software. In this paper, we present PracAttest, a practical runtime attestation framework for embedded devices running compute-heavy EdgeML applications. Unlike the conventional remote attestation…
Ismi Abidi, Vireshwar Kumar, Rijurekha Sen
ACSAC 2021
CORE A
SpotOn: Adversarially Robust Keyword Spotting on Resource-Constrained IoT Platforms
Mehreen Jabeen, Vireshwar Kumar, Rijurekha Sen
ACM AsiaCCS 2024 CORE A
SPAT: Semantic-Preserving Adversarial Transformation for Perceptually Similar Adversarial Examples
Subrat Kumar Swain, Vireshwar Kumar, Dan Dongseong Kim, Guangdong Bai
ECAI 2023 CORE A
PANDA: Practical Adversarial Attacks Against Intrusion Detection Applications
Subrat Kumar Swain, Vireshwar Kumar, Guangdong Bai, Dan Dongseong Kim
DSN Disrupt 2024 CORE A
Practical Attestation for Edge Devices Running Compute Heavy Machine Learning Applications
Ismi Abidi, Vireshwar Kumar, Rijurekha Sen
ACSAC 2021 CORE A
 SPRING @ Kripalani Lab